
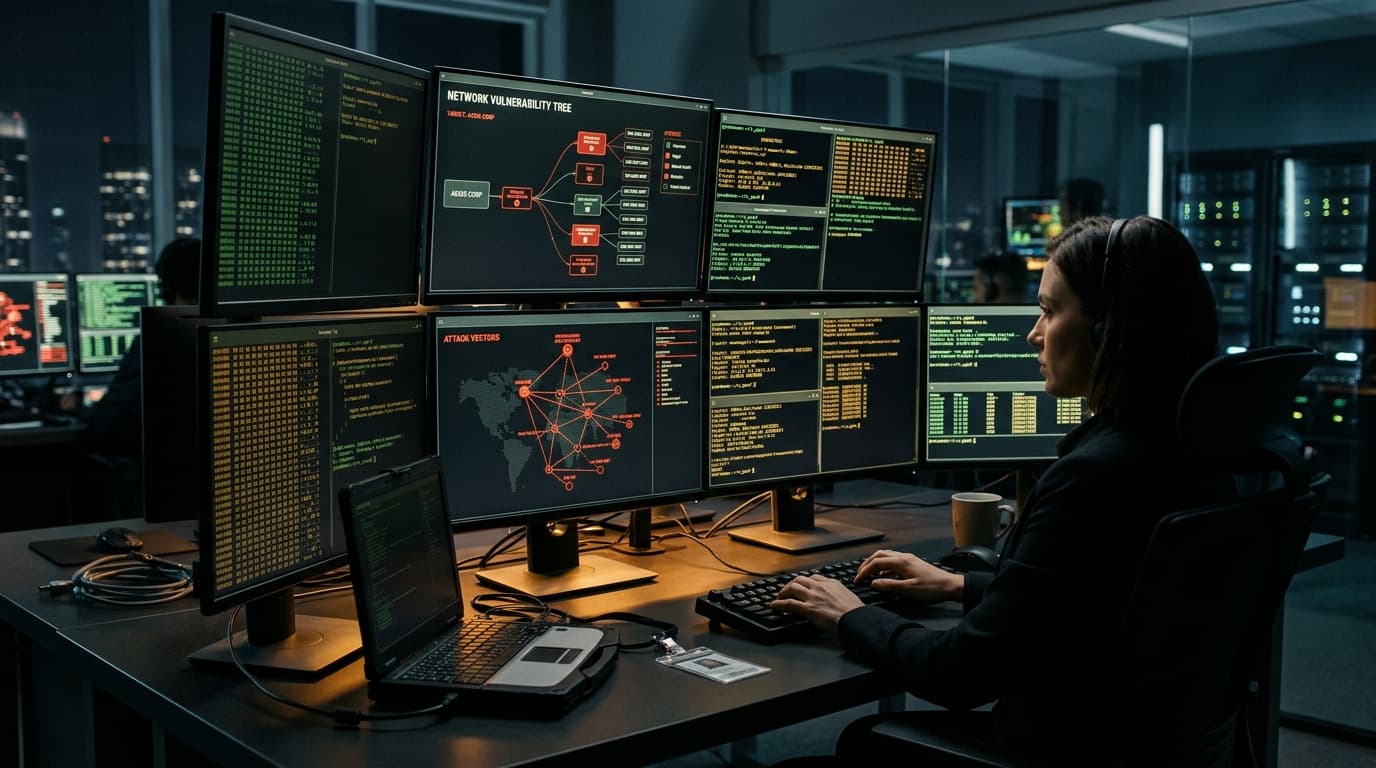
24x7 TOC monitoring (Threat Hunting)
Proactive Threat Operations Center human-led threat hunting searching for persistent attackers who evade automated signature detections.
Proactive Threat Operations Center human-led threat hunting searching for persistent attackers who evade automated signature detections. MAGEN delivers this as a scoped SOC & Incident Response mandate with senior practitioners, evidence-ready reporting, and a clear remediation path so leadership can act on findings without delay.
- Hypothesis-Driven Threat Hunting Campaigns
- Indicator of Attack (IOA) & Living-off-the-Land (LotL) Tracking
- Memory Dump Analysis & Kernel-Level Rootkit Hunts
- Custom Hunting Playbooks Aligned to MITRE ATT&CK
Map assets, controls, and business context so the engagement is bounded and measurable.
Senior specialists run the work, collect evidence, and document findings in executive and technical form.
Prioritised actions, owner-ready guidance, and validation so residual risk is closed or accepted.
Ready to build your next software initiative with embedded security?
Whether you are preparing for enterprise compliance audits, refactoring critical cloud infrastructure, or launching a brand-new application — MAGEN delivers sovereign-grade engineering practices tailored to your sector's most pressing requirements.