
SOC, Incident Response and Business Continuity
Round-the-Clock Monitoring, Threat Hunting & Rapid Emergency Containment
Enterprise 24x7 security operations, real-time threat detection, rapid containment playbooks, and business continuity resilience. Our NOC, SOC, and TOC operate continuously — triaging alerts, hunting persistent threats, and dispatching senior analysts on a sub-15-minute SLA.
24x7 NOC monitoring
Continuous Network Operations Center oversight tracking uptime, bandwidth bottlenecks, latency spikes, and network hardware degradation.
- •Round-the-Clock Network Infrastructure Telemetry
- •High-Frequency Ping, Packet Loss & Bandwidth Health Alerts
- •Hardware Failover & Redundant Route Health Checks
- •Root Cause Analysis & Incident Escalation SLAs
24x7 SOC monitoring
Security Operations Center active 24/7/365 triaging SIEM alerts, correlating multi-source telemetry, and investigating security anomalies.
- •Real-Time SIEM/SOAR Rule Correlation & Alert Triage
- •Endpoint, Identity & Cloud Log Stream Ingestion
- •<15 Minute SLA for Critical Incident Escalations
- •False-Positive Tuning & Detection Engineering
24x7 TOC monitoring (Threat Hunting)
Proactive Threat Operations Center human-led threat hunting searching for persistent attackers who evade automated signature detections.
- •Hypothesis-Driven Threat Hunting Campaigns
- •Indicator of Attack (IOA) & Living-off-the-Land (LotL) Tracking
- •Memory Dump Analysis & Kernel-Level Rootkit Hunts
- •Custom Hunting Playbooks Aligned to MITRE ATT&CK
Cloud Security Posture Management
Automated real-time CSPM monitoring compliance drift, IAM misconfigurations, and newly exposed cloud assets across all accounts.
- •Continuous Multi-Cloud Configuration Compliance Auditing
- •Automated Remediation of High-Risk Drift
- •Asset Inventory Discovery & Shadow IT Detection
- •Regulatory Posture Scoring (CIS, NIST, HIPAA, PCI)
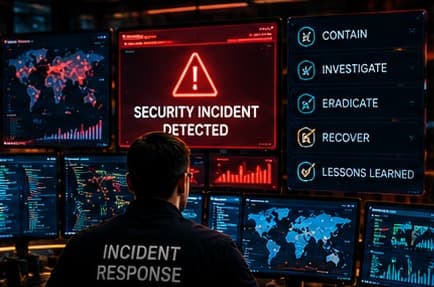
Incident Response
Immediate emergency dispatch for active breaches, forensics investigation, adversary containment, malware eradication, and recovery.
- •Emergency Forensic Isolation & Adversary Eviction
- •Digital Evidence Preservation & Chain of Custody
- •Malware Reverse Engineering & C2 Communication Analysis
- •Post-Incident Root Cause Report & Regulatory Breach Notification Dossier
Reporting & Analysis
Comprehensive monthly, quarterly, and executive security reporting detailing threat metrics, dwell time, and posture evolution.
- •Executive C-Suite Security Posture Briefings
- •Operational Metric Dashboards (MTTD, MTTR, Threat Volume)
- •Board-Ready Cyber Risk & Trend Presentations
- •Continuous Maturity & Recommendation Roadmaps
Ready to build your next software initiative with embedded security?
Whether you are preparing for enterprise compliance audits, refactoring critical cloud infrastructure, or launching a brand-new application — MAGEN delivers sovereign-grade engineering practices tailored to your sector's most pressing requirements.